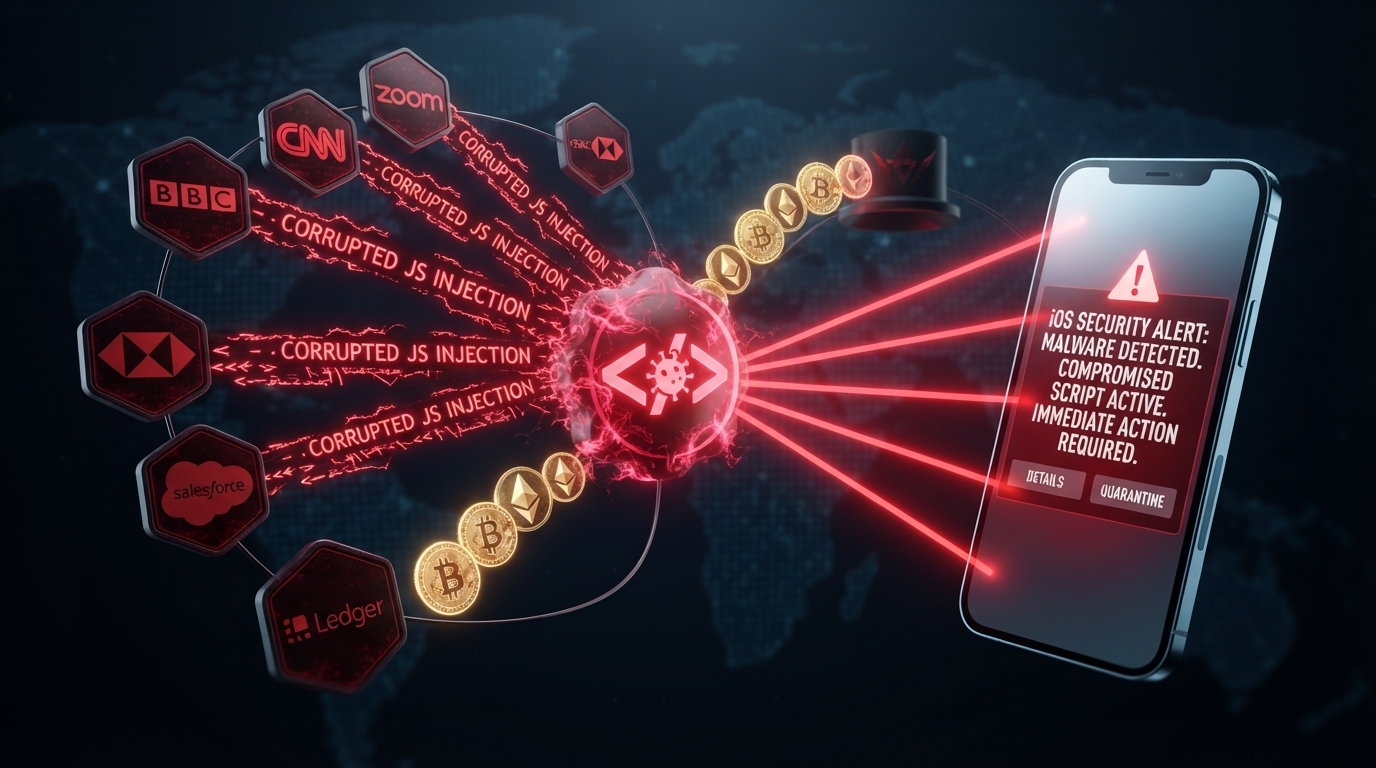
Visitors to the websites of 178 organisations, including Zoom, CNN, BBC, HSBC, IKEA and Ledger, were exposed to malicious code in a cyberattack designed to steal cryptocurrency, capture payment card details and target Apple devices.
The attack exploited Optimizely, a website experimentation platform used by businesses to test and personalise their websites. Attackers injected malicious JavaScript into customer projects, causing affected websites to load malware through scripts delivered by the platform.
Security researcher Scott Helme of Report URI identified 188 infected JavaScript snippets linked to 178 organisations after examining 1,611 Optimizely scripts.
Other organisations identified in the investigation include Salesforce, GitLab, Equifax, Air France-KLM and Peacock.
The incident is a supply-chain attack, where hackers compromise a third-party service or software used by other organisations to reach their customers and users.
How the malware targeted website visitors
The malicious JavaScript was designed to carry out several activities, depending on the visitor’s device and the website they accessed.
One of its main functions was cryptocurrency address replacement. The malware monitored web pages for cryptocurrency wallet addresses and attempted to replace legitimate addresses with ones controlled by the attackers.
This could cause users to send funds to the wrong wallet when copying and pasting a payment address.
The code also attempted to capture credit card numbers, expiry dates and security codes entered into website forms. It could additionally collect browser cookies, page URLs and screenshots, potentially exposing sensitive browsing information.
For iPhone and iPad users, the malware attempted to deliver exploit code associated with two iOS exploit kits, Coruna and DarkSword. These tools target vulnerabilities in Apple’s mobile operating systems and could put devices running vulnerable software at risk.
The attack therefore extended beyond cryptocurrency theft, potentially exposing website visitors to financial fraud and device compromise.
Optimizely confirms security incident
Optimizely confirmed that an unauthorised party exploited a vulnerability in its Experimentation account sign-up process to inject malicious JavaScript into some customer projects.
The company said it had blocked access to the vulnerable pathway, deployed a fix and removed the injected code from affected projects.
It also ended active sessions, revoked tokens, reset access for affected accounts and blocked the malicious code from being delivered through Cloudflare.
The company said it had notified affected customers and was continuing its investigation.
Salesforce also confirmed that it was investigating unauthorised changes to Optimizely scripts used on some of its websites. As a precaution, it disabled the scripts across its preview and production environments.
Were users’ funds already stolen?
Although the attack exposed visitors to several forms of malicious activity, the full extent of the damage remains unclear.
It was reported that it could not independently establish whether the malicious code had successfully compromised users across all affected websites or determine the overall impact.
However, blockchain records cited by Cointelegraph showed that cryptocurrency addresses associated with the malware had received approximately $7,100 on November 16, suggesting that at least some cryptocurrency theft had occurred.
The incident highlights the risks of relying on third-party website tools, particularly when those tools can execute JavaScript across pages visited by millions of people.
This is another reminder to verify wallet addresses carefully before confirming transactions. Users should also keep their devices and browsers updated, monitor payment accounts for suspicious activity and be cautious when entering sensitive information on websites.
Read also: Mozilla offers Nigerian tech builders a $100,000 fellowship without relocation