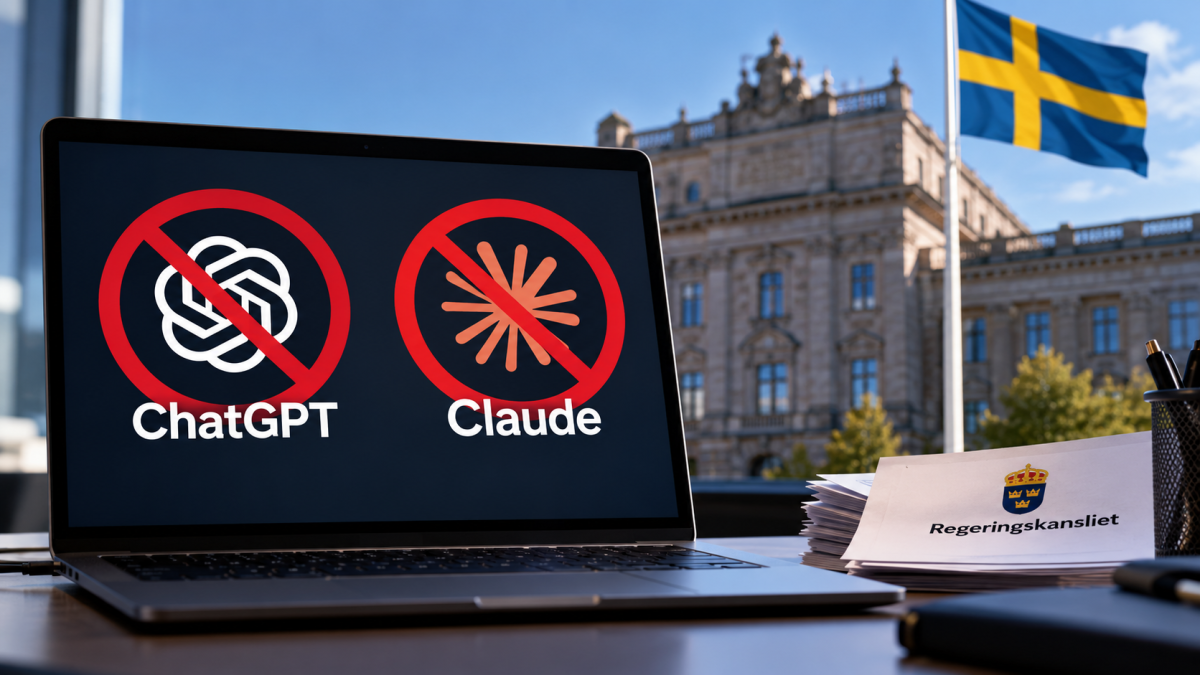
Sweden’s Government Offices will block staff access to ChatGPT and Claude from October 26, directing civil servants to approved AI tools, including Microsoft Copilot, over concerns about information security.
The decision, reported by Swedish public broadcaster Sveriges Radio on October 23, restricts direct access to the two AI services from government work computers. However, it does not amount to a complete ban on the underlying AI models, as some employees will retain access to ChatGPT and Claude through an internal AI platform.
The move highlights a growing challenge for governments and businesses adopting artificial intelligence: how to benefit from AI tools while protecting sensitive information and maintaining control over how employees use them.
Why Sweden is restricting ChatGPT and Claude
Mikael Wettercrantz, director of digitalisation at the Government Offices, said the organisation had observed problematic use of open AI services.
According to comments reported by Sveriges Radio, the concerns included the sensitivity of information entered into these services and how employees handled the AI-generated responses.
Using AI tools without a formal agreement can have consequences for information security, Wettercrantz said in a message shared on the organisation’s internal network.
The Government Offices supports Sweden’s prime minister and cabinet ministries, making the protection of government information a significant consideration.
Employees may use AI assistants to summarise documents, draft correspondence, research policy questions and organise information. However, entering confidential documents or sensitive information into an unapproved service can expose an organisation to risks it has not adequately assessed.
The concern is not limited to whether an AI model produces accurate answers. It also involves where information is processed, how it is handled, what contractual protections apply and who can access it.
A public-facing AI service and an enterprise deployment may use similar underlying technology while operating under different contractual terms, administrative controls and data-protection arrangements.
Sweden’s decision reflects an effort to ensure staff use services that the government has reviewed and approved.
Why Microsoft Copilot remains approved
While ChatGPT and Claude are being blocked on staff computers, Microsoft Copilot remains available as an approved alternative.
The Government Offices said it had reviewed Copilot and subsequently strengthened its security settings.
The distinction is important because the decision is not necessarily a judgment that ChatGPT and Claude are inherently insecure while Copilot is inherently safe.
Instead, it concerns the specific services, configurations, agreements and safeguards approved for government use.
An organisation may accept a particular AI tool after reviewing its data-handling practices, access controls and contractual protections. The same organisation may restrict another tool if it has not completed the necessary assessment or established acceptable conditions for its use.
Microsoft’s Copilot products also operate in different configurations, meaning the security and privacy protections available can depend on the specific product and organisational setup.
However, the decision has raised an additional question: what happens when an approved AI tool can use models developed by a company whose standalone service is restricted?
The Claude connection raises questions
Microsoft has made Anthropic’s Claude models available within certain Copilot experiences. This creates an apparent contradiction in Sweden’s decision to block direct access to Claude while permitting Copilot.
However, the distinction between an AI model and the service through which it is accessed matters.
An AI model is the underlying technology that generates responses. An AI application provides the interface, infrastructure, permissions and controls through which people use that model.
Two applications can therefore provide access to similar models while handling user information under different technical and contractual arrangements.
For example, an organisation may allow employees to use a model through a centrally managed platform that applies access restrictions and administrative policies. It may still prohibit employees from accessing a separate consumer service directly.
In Sweden’s case, the Government Offices has not confirmed whether Claude models are enabled in its approved Copilot deployment. Their availability should therefore not be treated as established.
The organisation has also said that some employees will continue to access ChatGPT and Claude through an internal AI platform.
This means the restrictions concern the routes through which employees access AI services, rather than eliminating every possible use of the models themselves.
Sweden is not alone in restricting AI services
The decision follows similar measures elsewhere in Sweden’s public sector.
According to Sveriges Radio, the Swedish Tax Agency and the National Board of Institutional Care have introduced restrictions on certain AI services. The Swedish Enforcement Authority is also considering its position.
An internal audit at the Swedish Transport Administration previously identified widespread and risky use of multiple AI services.
These developments point to a broader challenge for public institutions. Employees may adopt AI tools to work faster, even when their organisations have not established clear policies governing what information can be shared or which services can be used.
Without those policies, staff may unintentionally expose sensitive information or rely on AI-generated material without sufficient verification.
Blocking specific services is one way to reduce that risk. Other measures include providing approved alternatives, training employees, implementing technical controls and establishing clear rules for handling confidential information.
The goal is to make AI use more controlled without necessarily abandoning its potential benefits.
What this means for businesses adopting AI
Sweden’s decision offers several lessons for companies integrating AI into their operations.
First, organisations need an AI usage policy. Employees should understand which tools are approved, what information they may enter and when human review is required.
Second, businesses should assess AI services before deploying them. This includes examining data retention, access permissions, contractual commitments and whether information may be used to improve a provider’s models.
Third, companies should not assume that an AI tool is safe simply because it is popular or comes from a familiar technology provider. Security depends on the particular service, configuration and controls in place.
Finally, organisations need to distinguish between banning AI and governing its use. Employees who lose access to one tool may simply turn to another unless their organisation provides clear guidance and workable alternatives.
For businesses, the answer is not necessarily to block every external AI service. It is to establish controls that reflect the sensitivity of the information being handled and the consequences of unauthorised disclosure.
AI adoption increasingly depends on trust
Sweden’s restrictions illustrate how AI governance is becoming an operational issue rather than just a discussion about innovation.
Governments and businesses want employees to benefit from AI, but they also need to protect sensitive information, maintain accountability and understand how external services handle their data.
The distinction between ChatGPT, Claude and Copilot in this case is not simply about which model produces the best response. It is about which access arrangements and security controls an organisation is prepared to approve.
As AI tools become more deeply integrated into everyday work, organisations will need policies that address both the technology and the way employees use it.The challenge is to make AI adoption productive without allowing convenience to undermine information security.