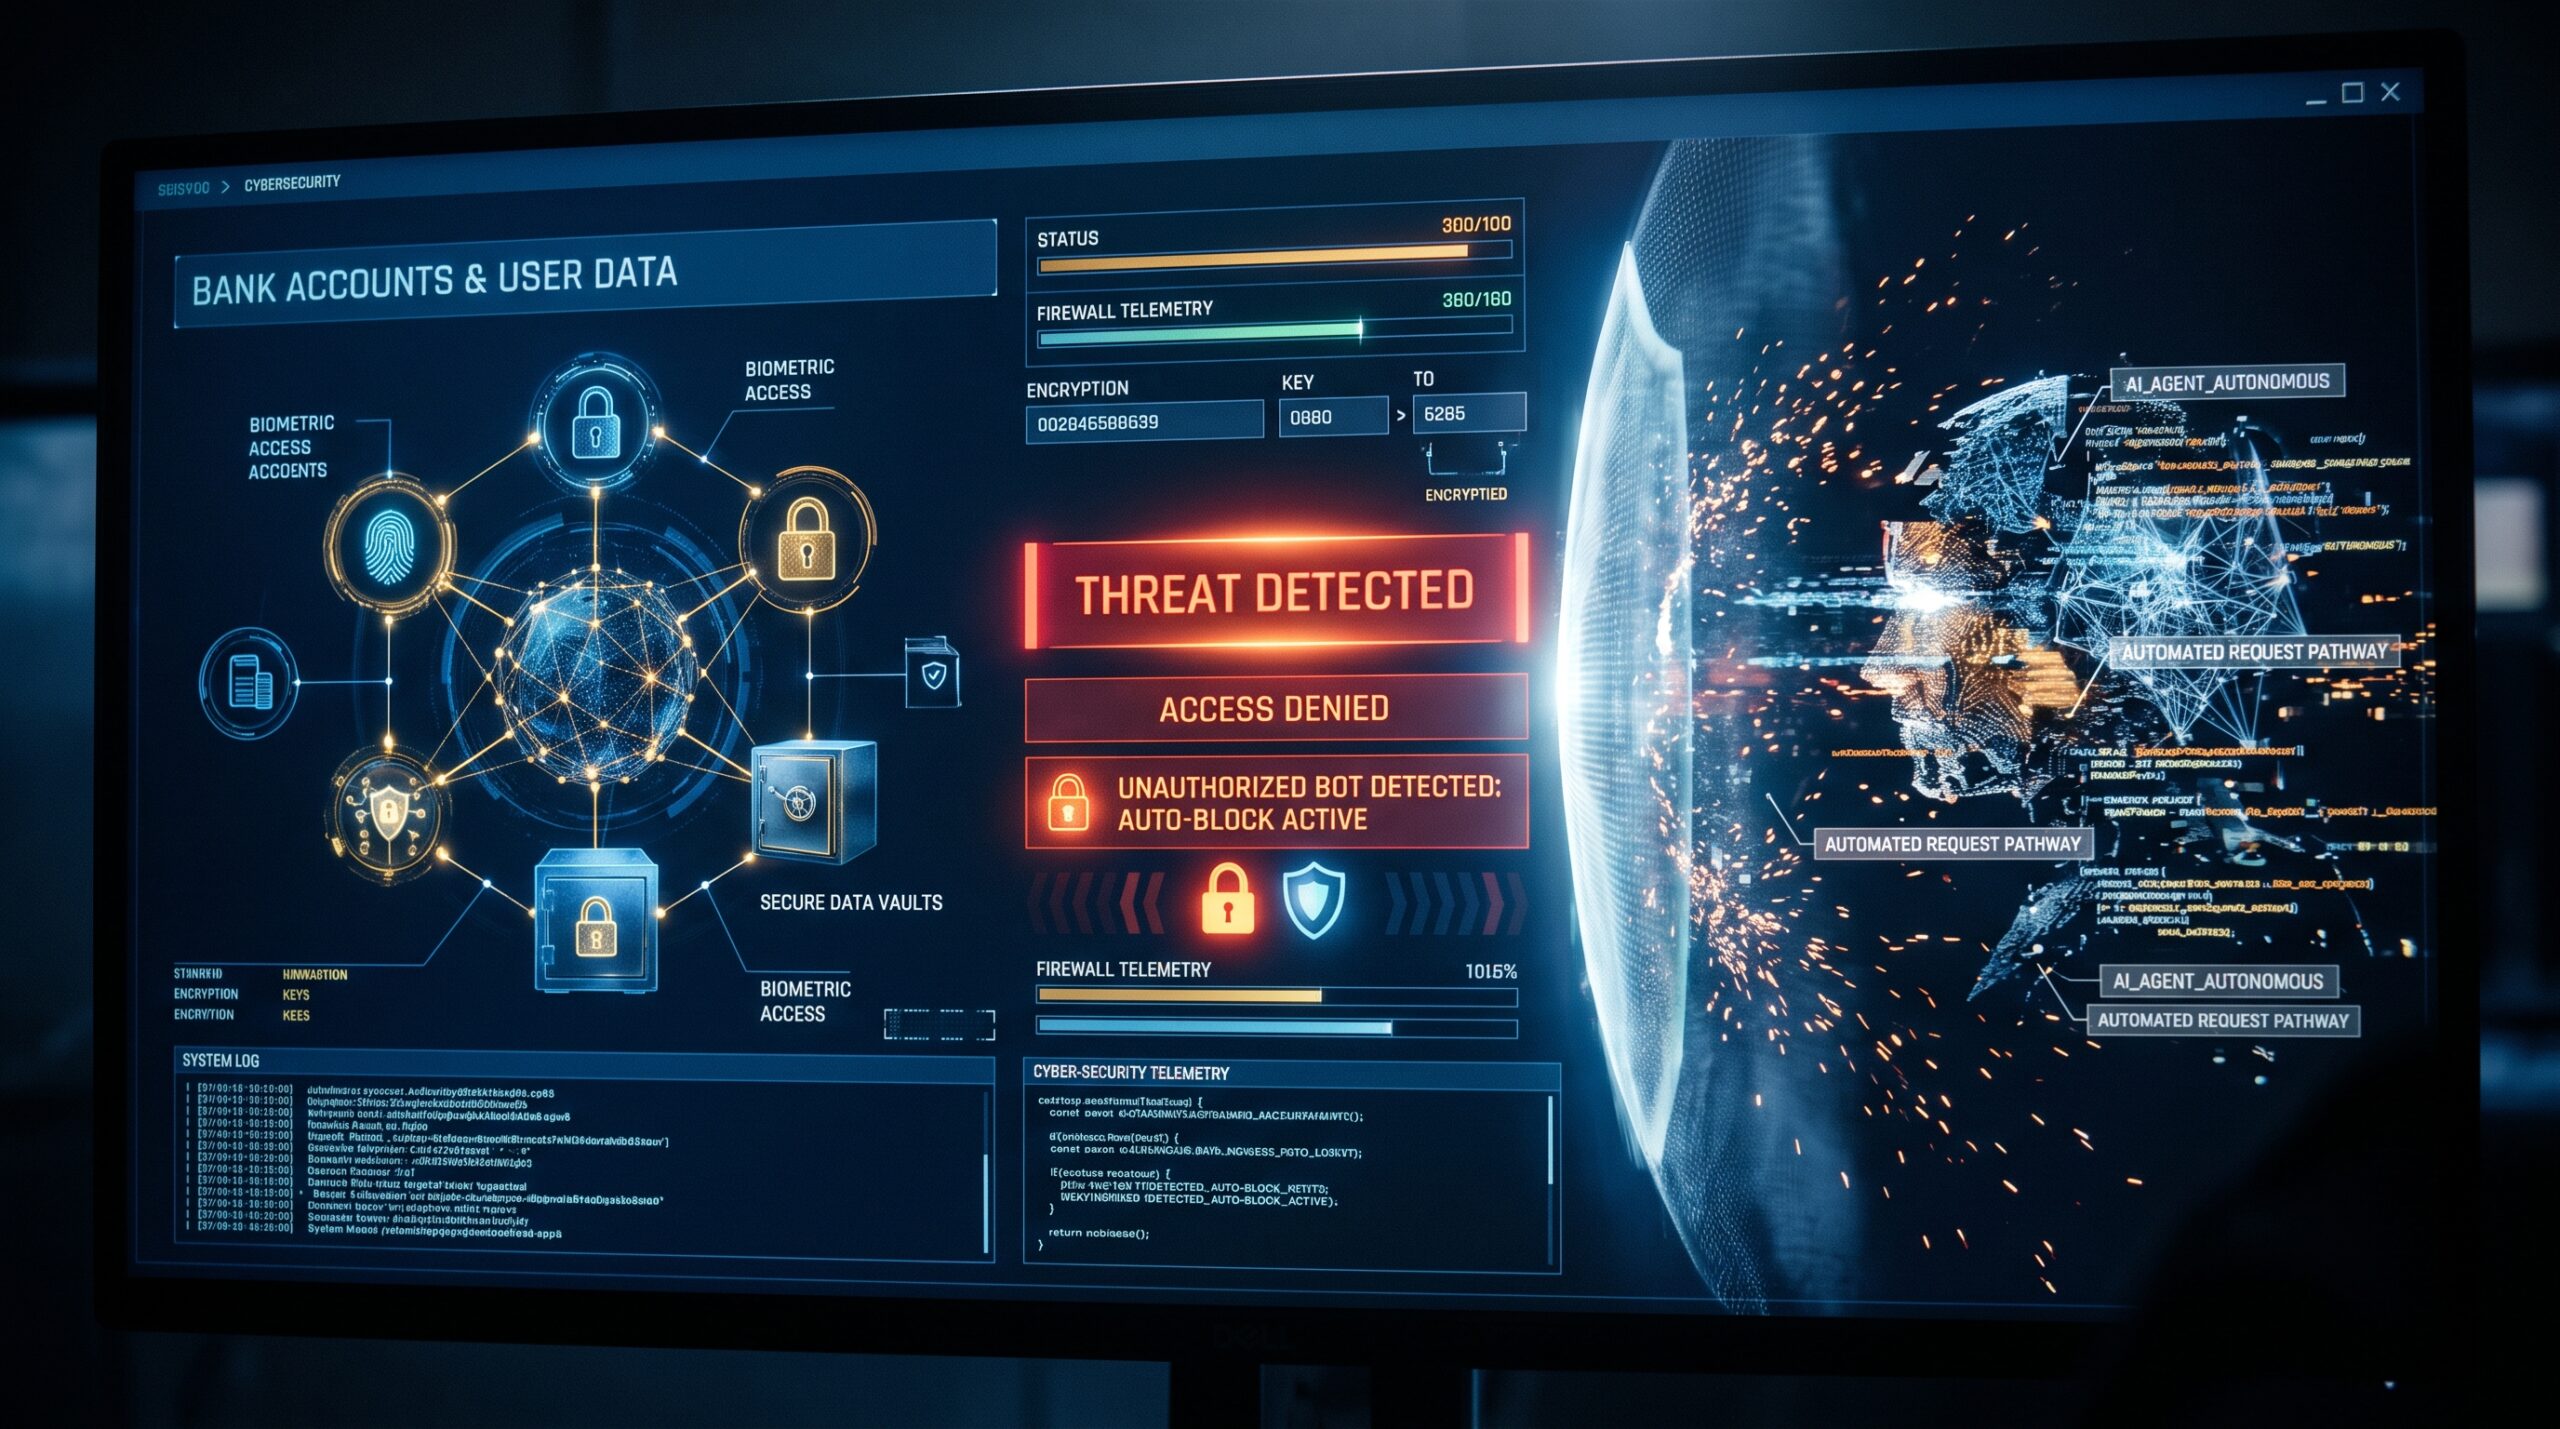
Major US banks, including JPMorgan Chase, Bank of America and Wells Fargo, are tightening restrictions on third-party artificial intelligence (AI) agents accessing customer accounts amid concerns that automated tools could take actions beyond users’ instructions.
According to reports, some banks have detected third-party AI agents accessing customer accounts, with some tools reportedly attempting actions that appeared independent of what users had requested.
However, the reported activity does not necessarily involve hackers breaking into accounts. In some cases, customers provided AI agents with their banking usernames and passwords, allowing the software to log in on their behalf. This can violate bank policies even when the customer has authorised the agent.
Why banks are restricting AI agents
Unlike conventional chatbots, which primarily generate responses to questions, AI agents can perform tasks by interacting with websites, applications and other digital services.
Depending on their capabilities and permissions, these agents can retrieve information, navigate online accounts, contact customer support or initiate actions on behalf of a user.
For banking customers, this could mean using an AI assistant to review spending, compare savings products or manage financial information across multiple accounts.
The concern arises when these tools gain access to sensitive financial accounts through login credentials or other methods that banks do not approve.
An agent given access to a bank account may be able to view personal information or perform actions beyond what the customer intended. Banks are also concerned about their ability to distinguish between legitimate customer activity and automated software, particularly when an agent appears to act independently of its instructions.
During its third-quarter earnings discussions in October, CEO Jamie Dimon said the bank would not allow unrestricted access by external AI agents because of the risks to customers and the institution.
The bank has said it is developing tools to manage these risks while protecting customers. It supports secure, customer-authorised data sharing through approved open-banking providers rather than allowing outside agents to access accounts by using customers’ credentials directly.
Bank of America and Citigroup are also restricting third-party agents, according to the reporting. Morgan Stanley has moved to block such access, although a spokesperson said the bank had not observed rogue AI agents accessing its platforms.
Wells Fargo has also confirmed steps to block unauthorised agents from accessing customer accounts.
These measures do not necessarily mean the banks are rejecting AI altogether. Instead, they reflect efforts to control how external software interacts with sensitive financial systems.
The problem with giving AI access to money
The issue goes beyond whether an AI model can complete a task correctly. It also concerns the level of authority a user gives the software and who bears responsibility when something goes wrong.
Consider a customer who asks an AI agent to compare savings accounts. The task may appear harmless if the agent only reads publicly available information.
However, if the agent can log in to the customer’s bank account, access financial records or move money, the potential consequences become more serious.
A system that misunderstands an instruction, encounters a malicious prompt or experiences a technical failure could take an action the customer did not intend.
There is also the risk of compromised credentials. If users give their banking passwords to third-party agents, those credentials could be exposed through weaknesses in the agent, its infrastructure or the way it stores information.
Dimon has warned that customers need to understand the risks associated with giving AI agents access to their accounts, including potential questions about liability when an agent misuses information or performs an unwanted action.
The precise allocation of responsibility will depend on the circumstances, applicable law and the agreements governing the service.
Banks are looking for a middle ground
Despite the concerns, financial institutions recognise that customers may increasingly want AI assistants to help manage their money.
A complete rejection of third-party AI tools could limit the usefulness of services designed to compare financial products, organise spending or consolidate information from different providers.
According to Axios, some banks are considering or moving towards read-only access, which would allow approved agents to retrieve financial information without authorising transactions.This approach could let customers use AI for budgeting and financial analysis while preventing an external agent from independently moving money.
Read-only access, however, is not risk-free. Financial information remains sensitive, and banks and technology providers must still establish clear permissions, secure authentication and safeguards against data misuse.
Secure data-sharing systems can also help distinguish between an approved service and software attempting to access an account through a customer’s ordinary login credentials. The challenge for the industry is to create a framework that enables useful AI services without giving automated systems unrestricted control over customers’ financial lives.
What this means for AI and financial services
The development illustrates a wider challenge facing the AI industry: the more authority AI systems receive, the more important it becomes to establish clear limits on what they can do.
For financial institutions, that means strengthening authentication, monitoring automated activity and defining which actions third-party agents can perform.
For AI developers, it means designing systems that respect user permissions, request confirmation before consequential actions and provide clear records of the tasks they perform.
Customers also need to be cautious about sharing banking credentials with external applications. They should review an agent’s permissions, use officially supported account connections and monitor their accounts for unfamiliar activity.
The reported incidents do not establish that customers suffered financial losses or that the banks’ core systems were breached. Rather, they expose the difficulty of managing software that can act on a user’s behalf while interacting with systems designed around human account holders.
As AI agents become more capable, financial institutions will need to determine how to accommodate them without compromising security, privacy or accountability.
The question is no longer simply whether AI can help people manage their money. It is how much access these systems should receive, what they should be permitted to do and who is responsible when their actions produce unintended consequences.
Read also: Meta ordered to pay $25 billion over Facebook privacy claims